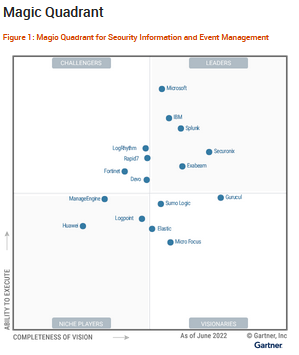
2022 Gartner Magic Quadrant for SIEM

SIEM aggregates the event data that is produced by monitoring, assessment, detection and response solutions deployed across application, network, endpoint and cloud environments. Capabilities include threat detection, through correlation and user and entity behavior analytics (UEBA), and response integrations commonly managed through security orchestration, automation and response (SOAR). Security reporting and continuously updated threat content through threat intelligence platform (TIP) functionality are also common integrations. Although SIEM is primarily deployed as a cloud-based service, it may support on-premises deployment.
GET YOUR FREE COPY:

    1. Salutation

    2. First Name

    3. Last Name

    4. Company

    5. Phone

    6. Job title/Position

    7. Email*

    8. Country

    9. State/Region

    10. ZIP

    11.  
    12. B2B Media Group GmbH Data privacy agreement

      I consent to the ascertainment, conversion, utilisation and dissemination of the data I have entered into this registration form. The B2B Media Group GmbH and originator/sponsor of the document may use my contact data for the purpose of B2B marketing (via e-mail, phone, display and postal) until such time as I withdraw my consent.

      My agreement to the company and our partner as shown above, can be revoked at any time via the Unsubscribe Link below:
      Unsubscribe.

    13.  
    14. IBM Data privacy agreement

      IBM may use my contact data to keep me informed of products, services and offerings:

    15. by Phone

    16. by Telephone

    17. via Post
       

    18. You can withdraw your marketing consent at any time by submitting an opt-out request. Also you may unsubscribe from receiving marketing emails by clicking the unsubscribe link in each email.

    19. More information on our processing can be found in the IBM Privacy Statement. By submitting this form, I acknowledge that I have read and understand the IBM Privacy Statement.